Overview
Curated abstract when available.
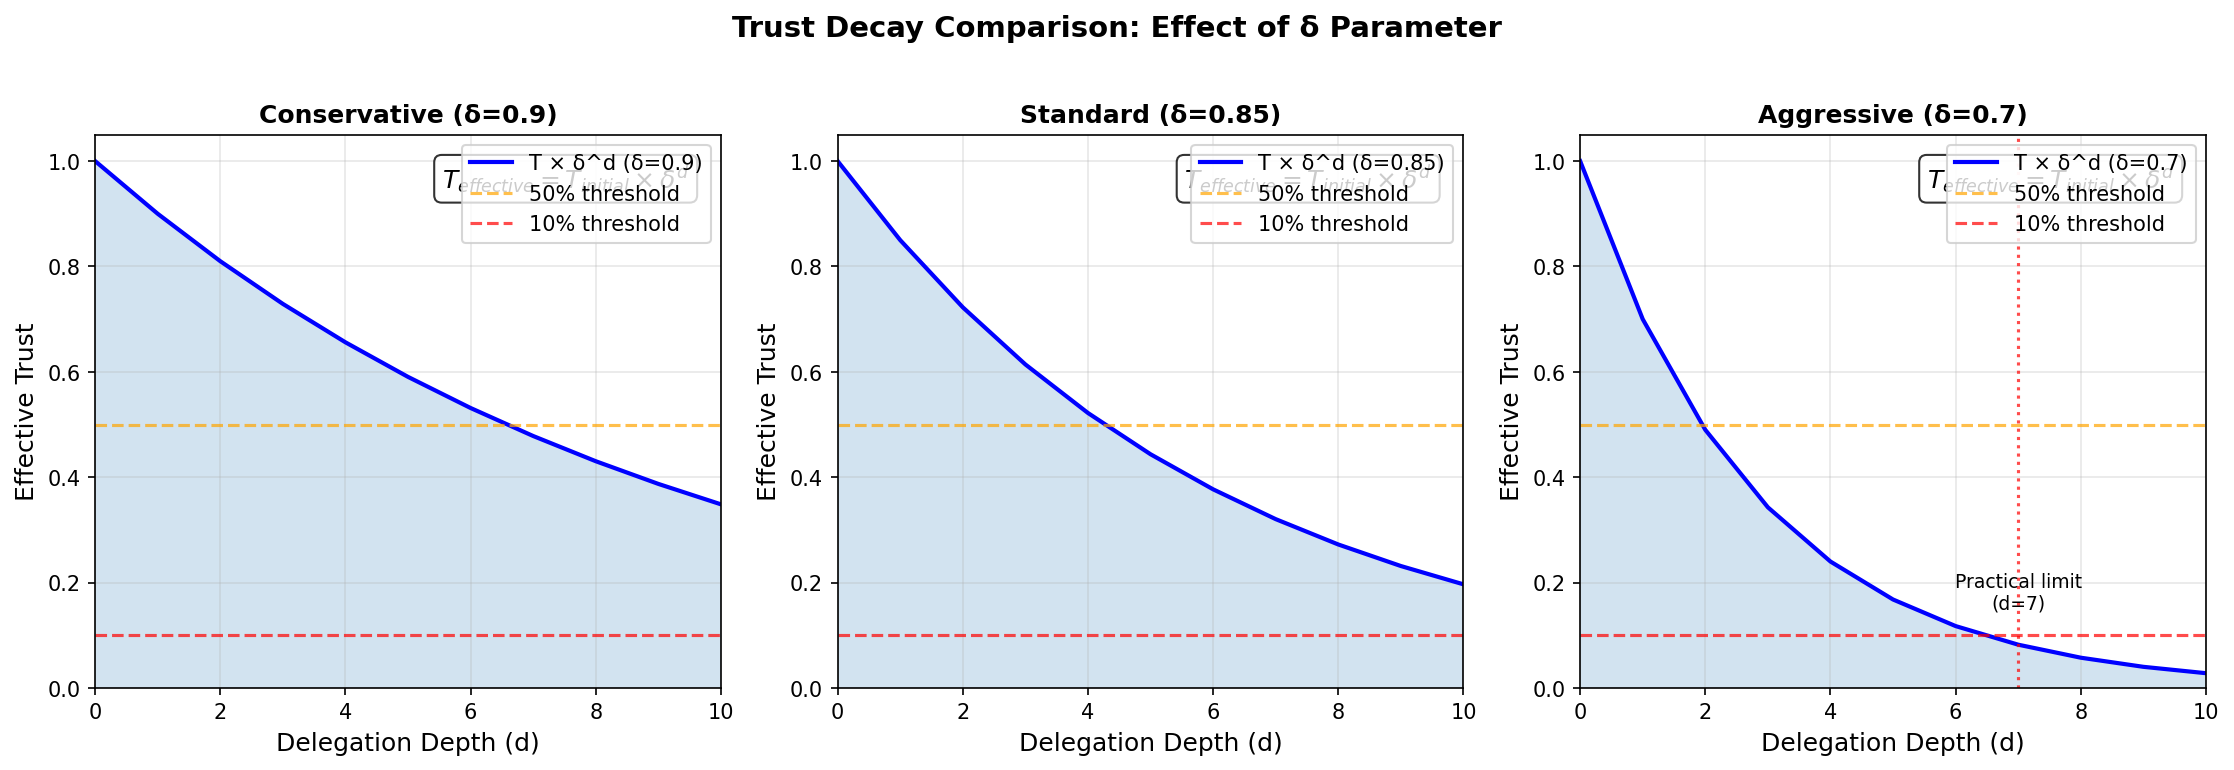
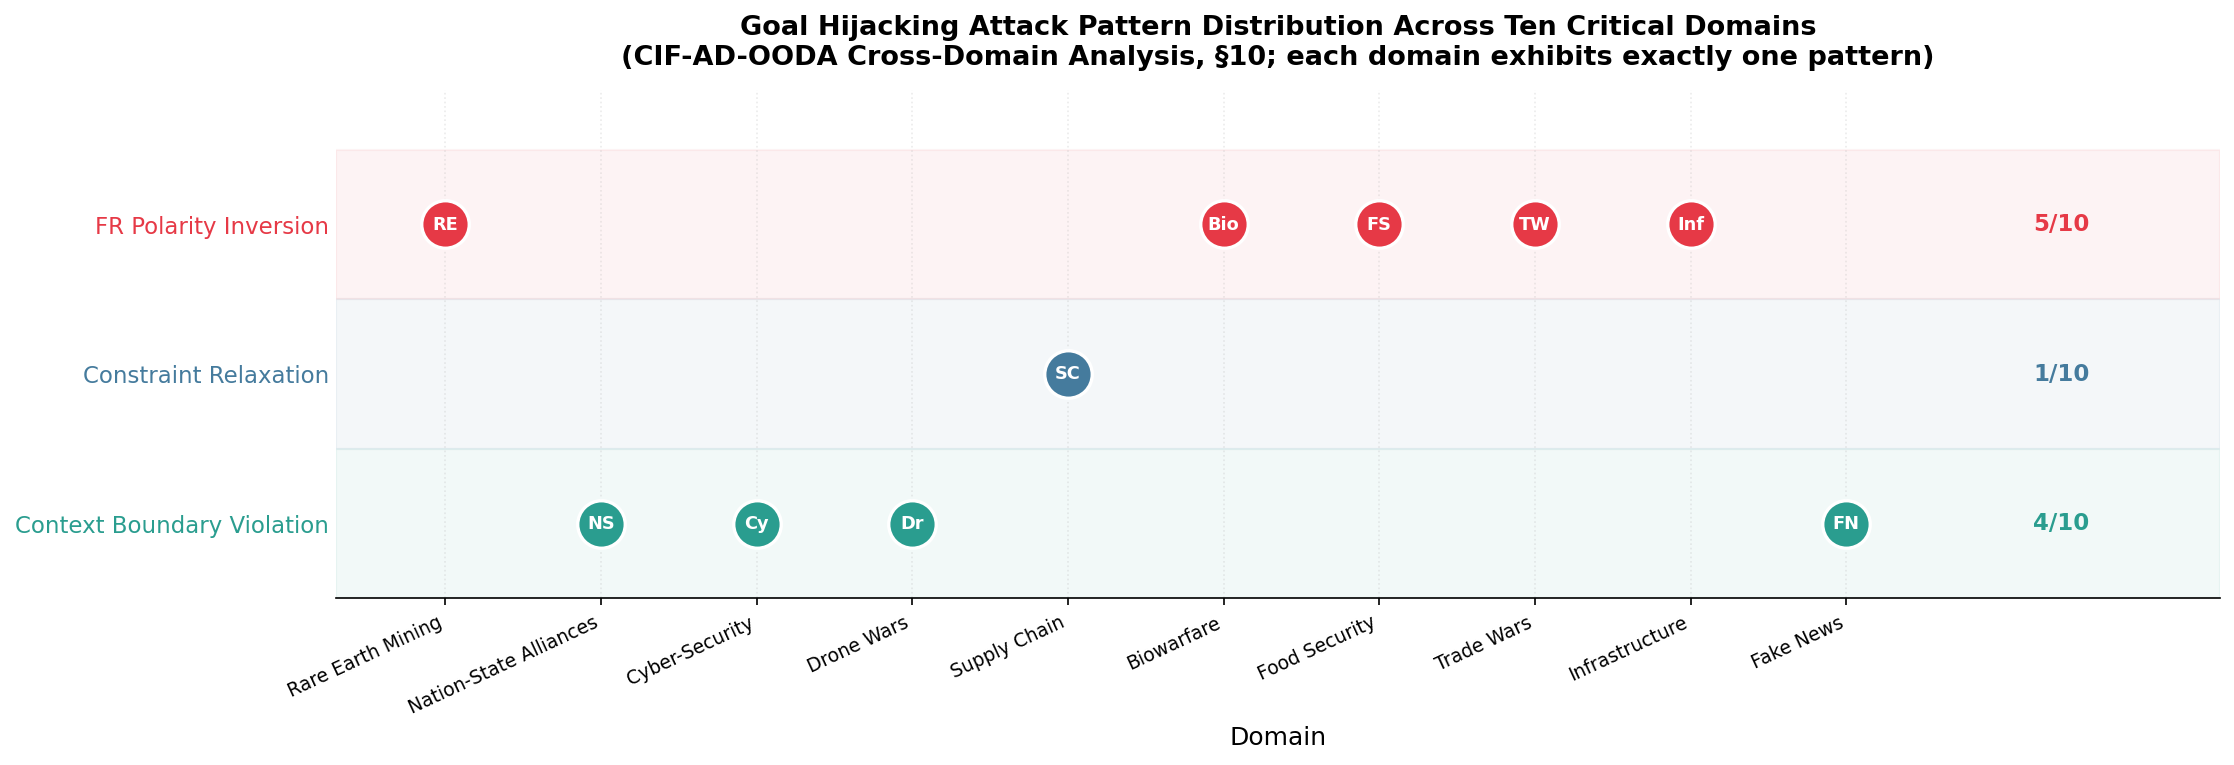
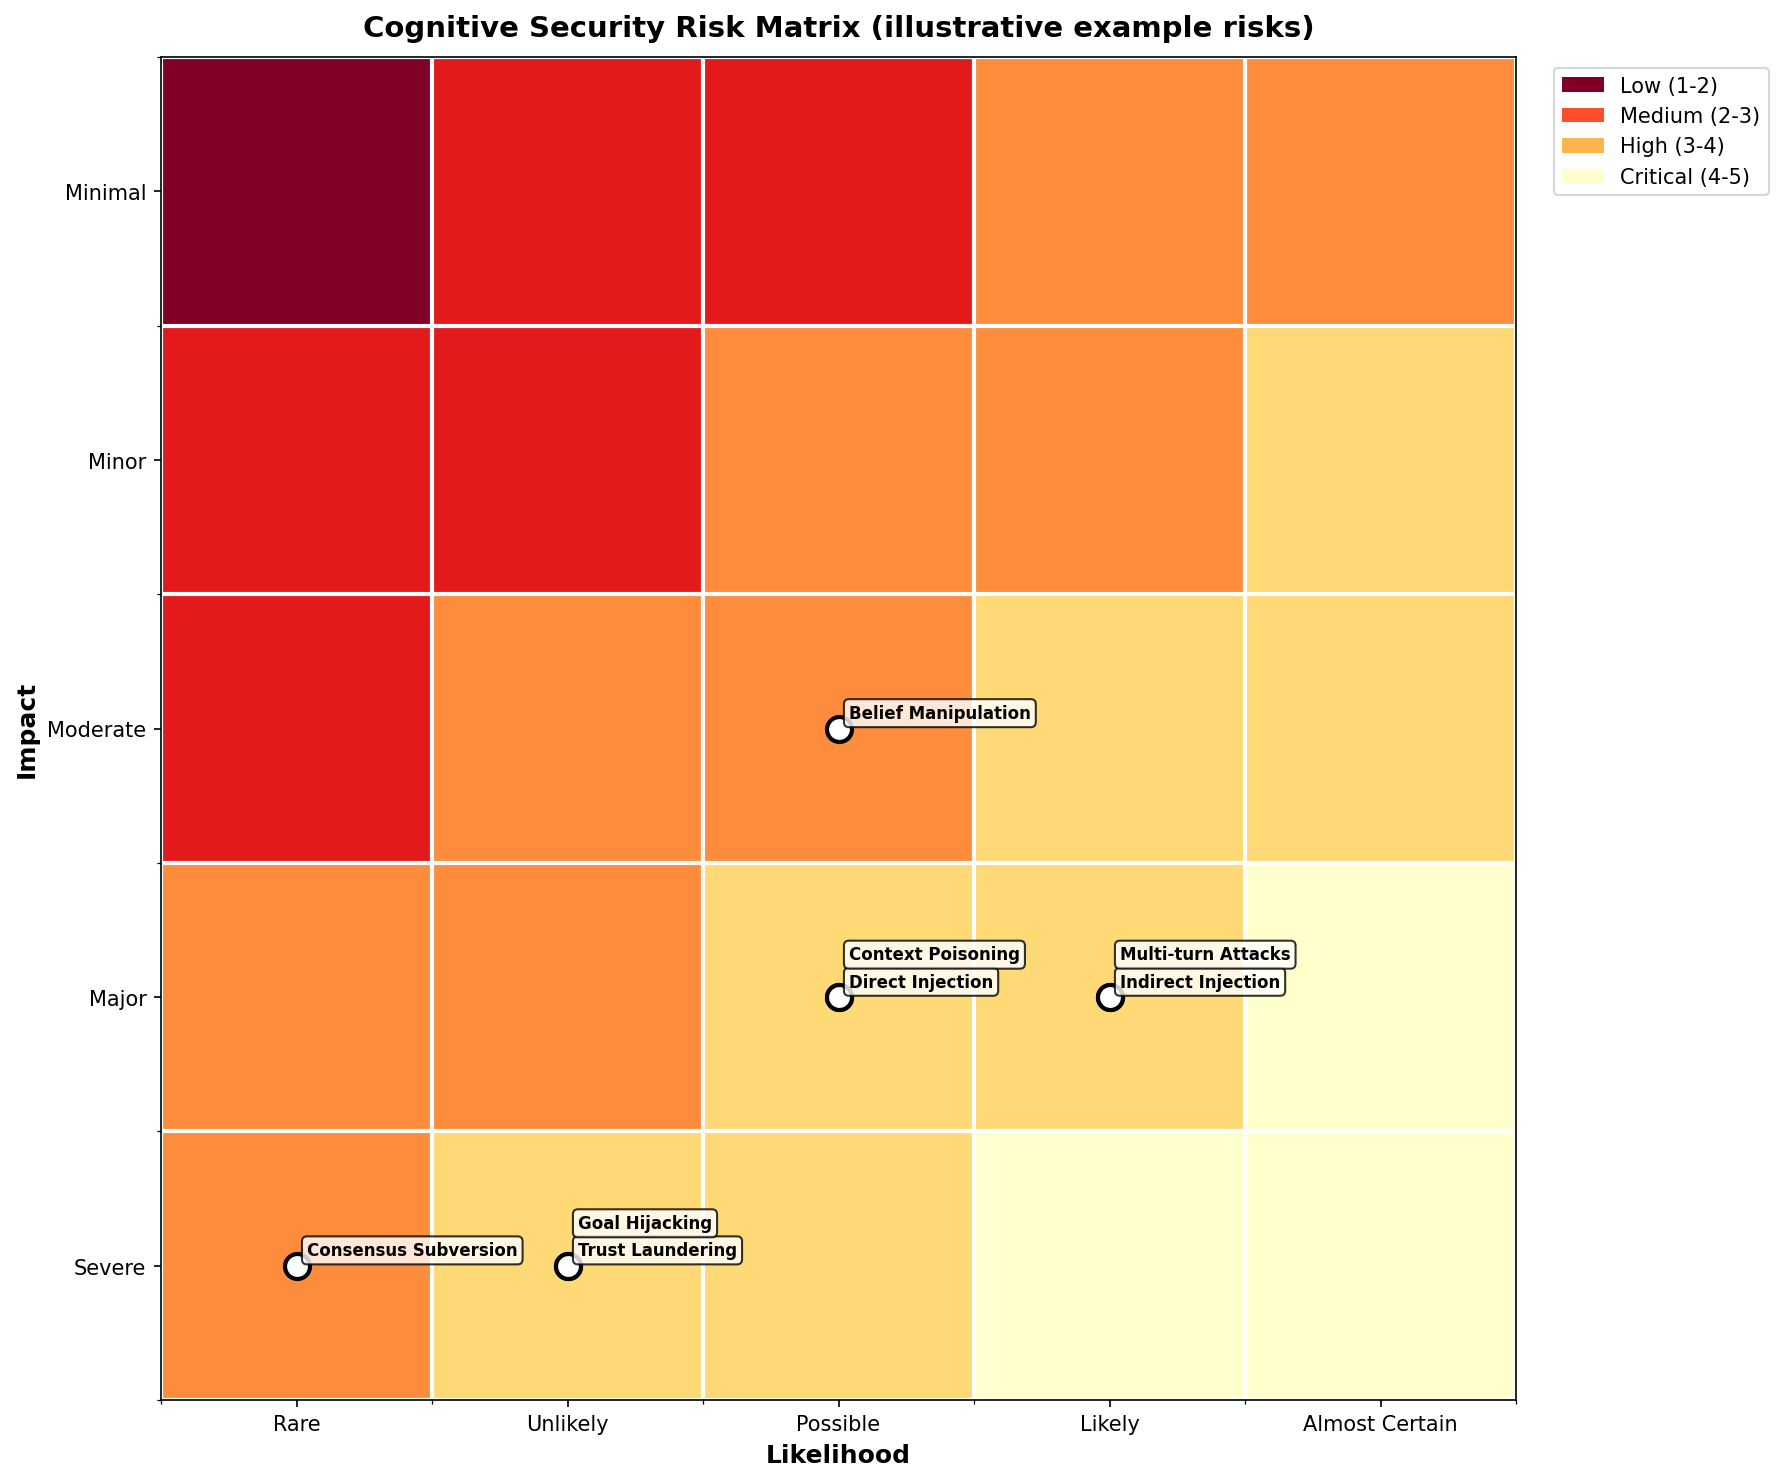
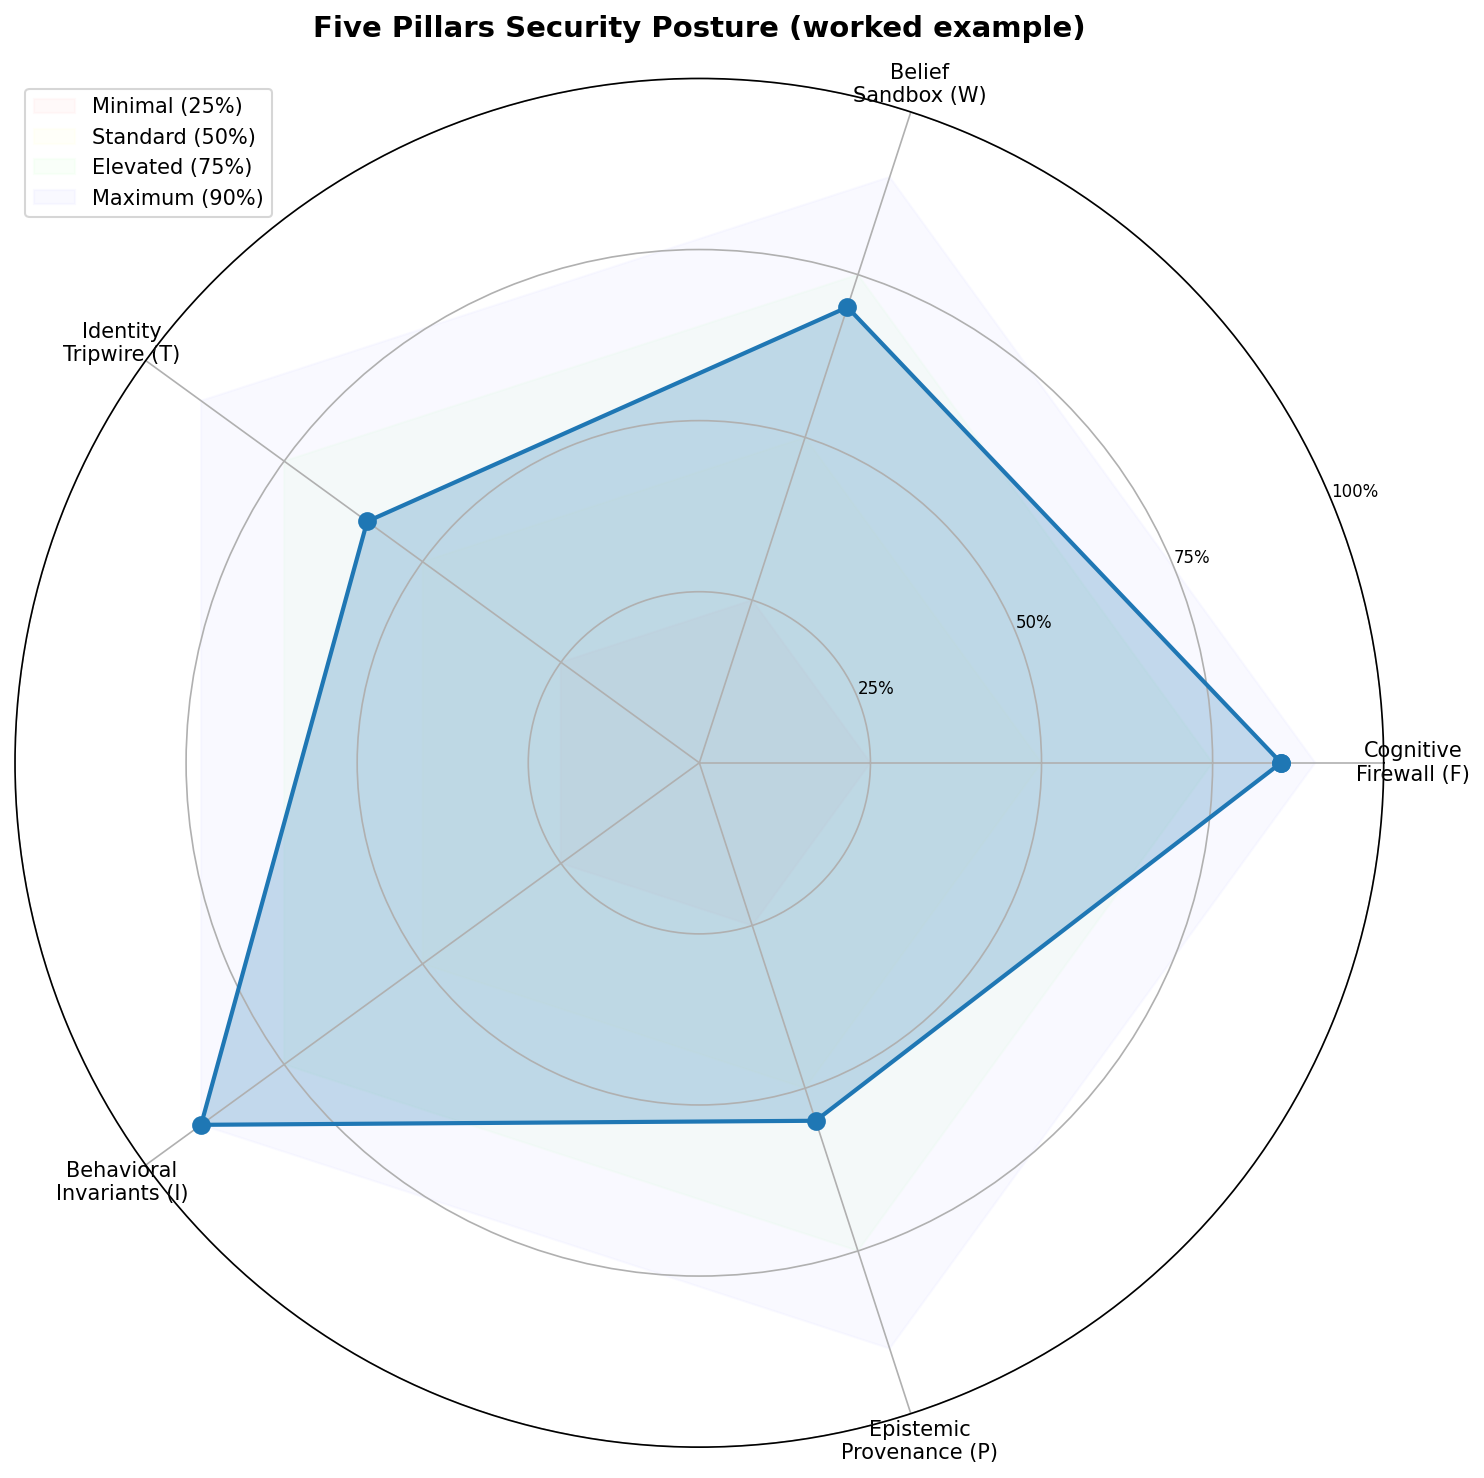
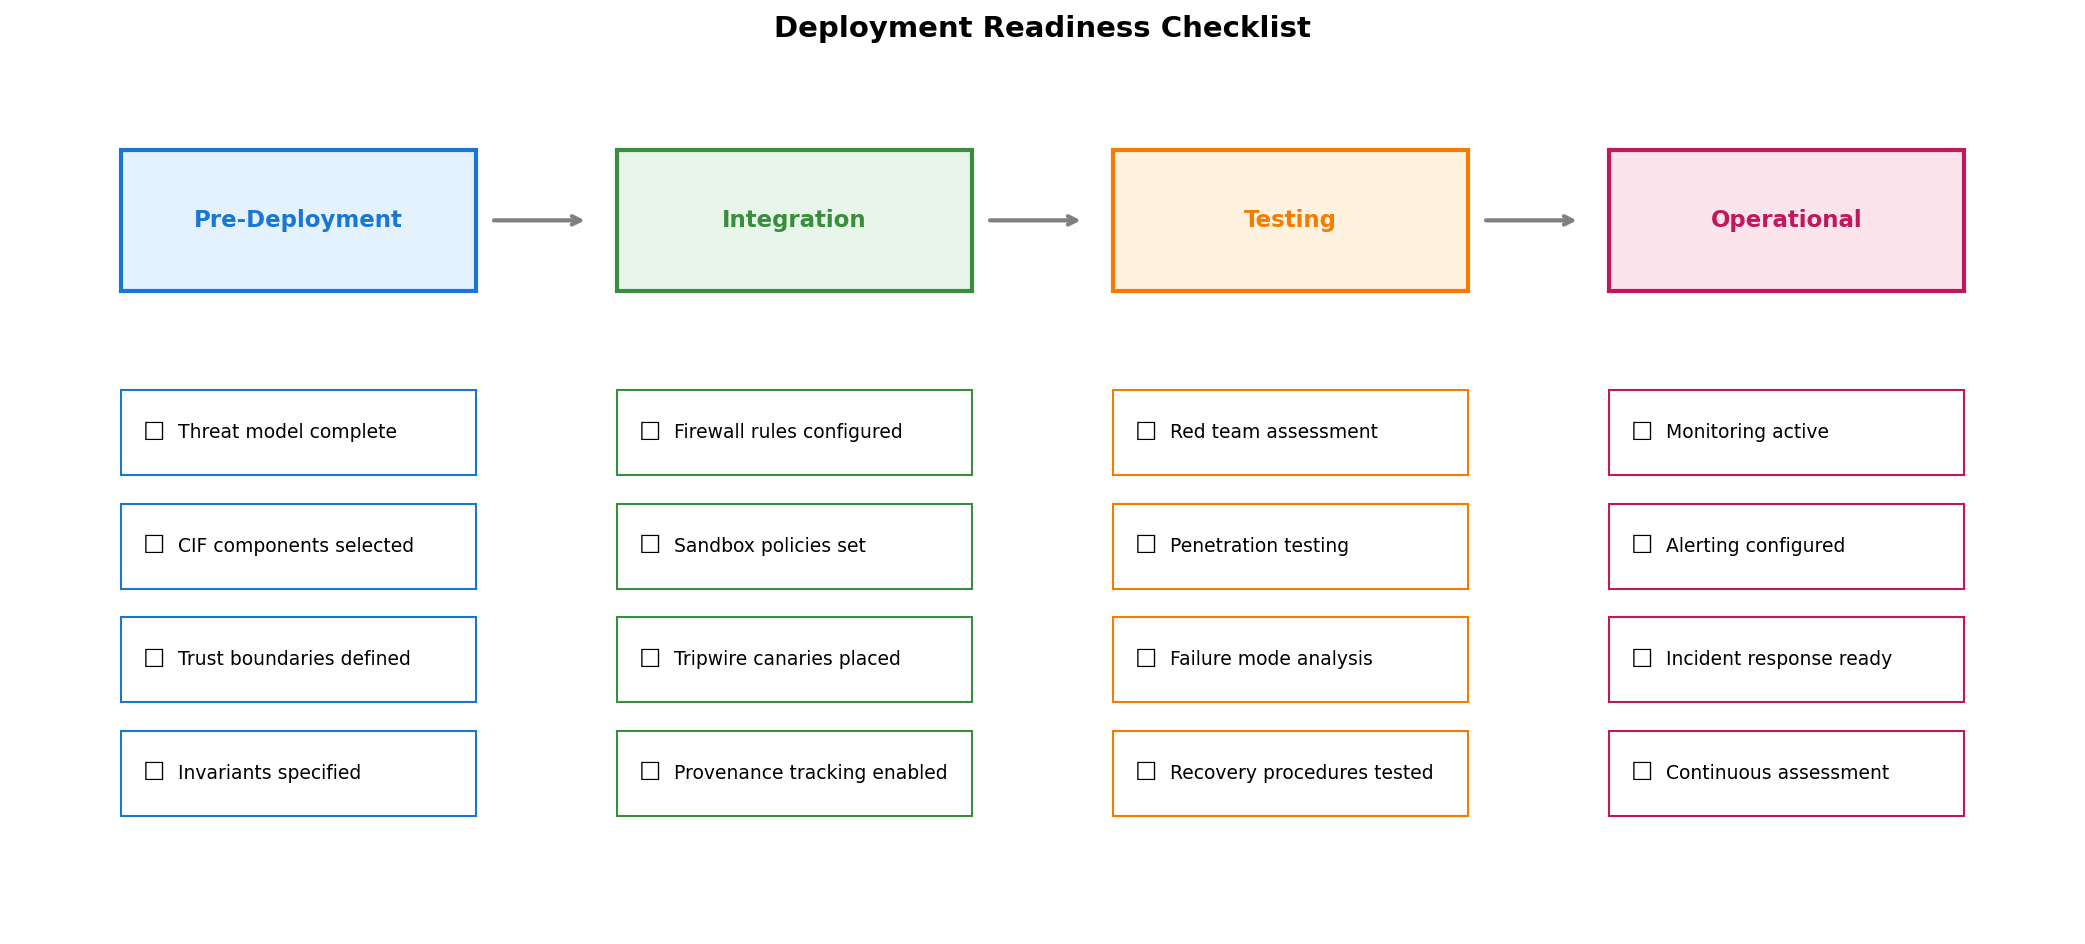
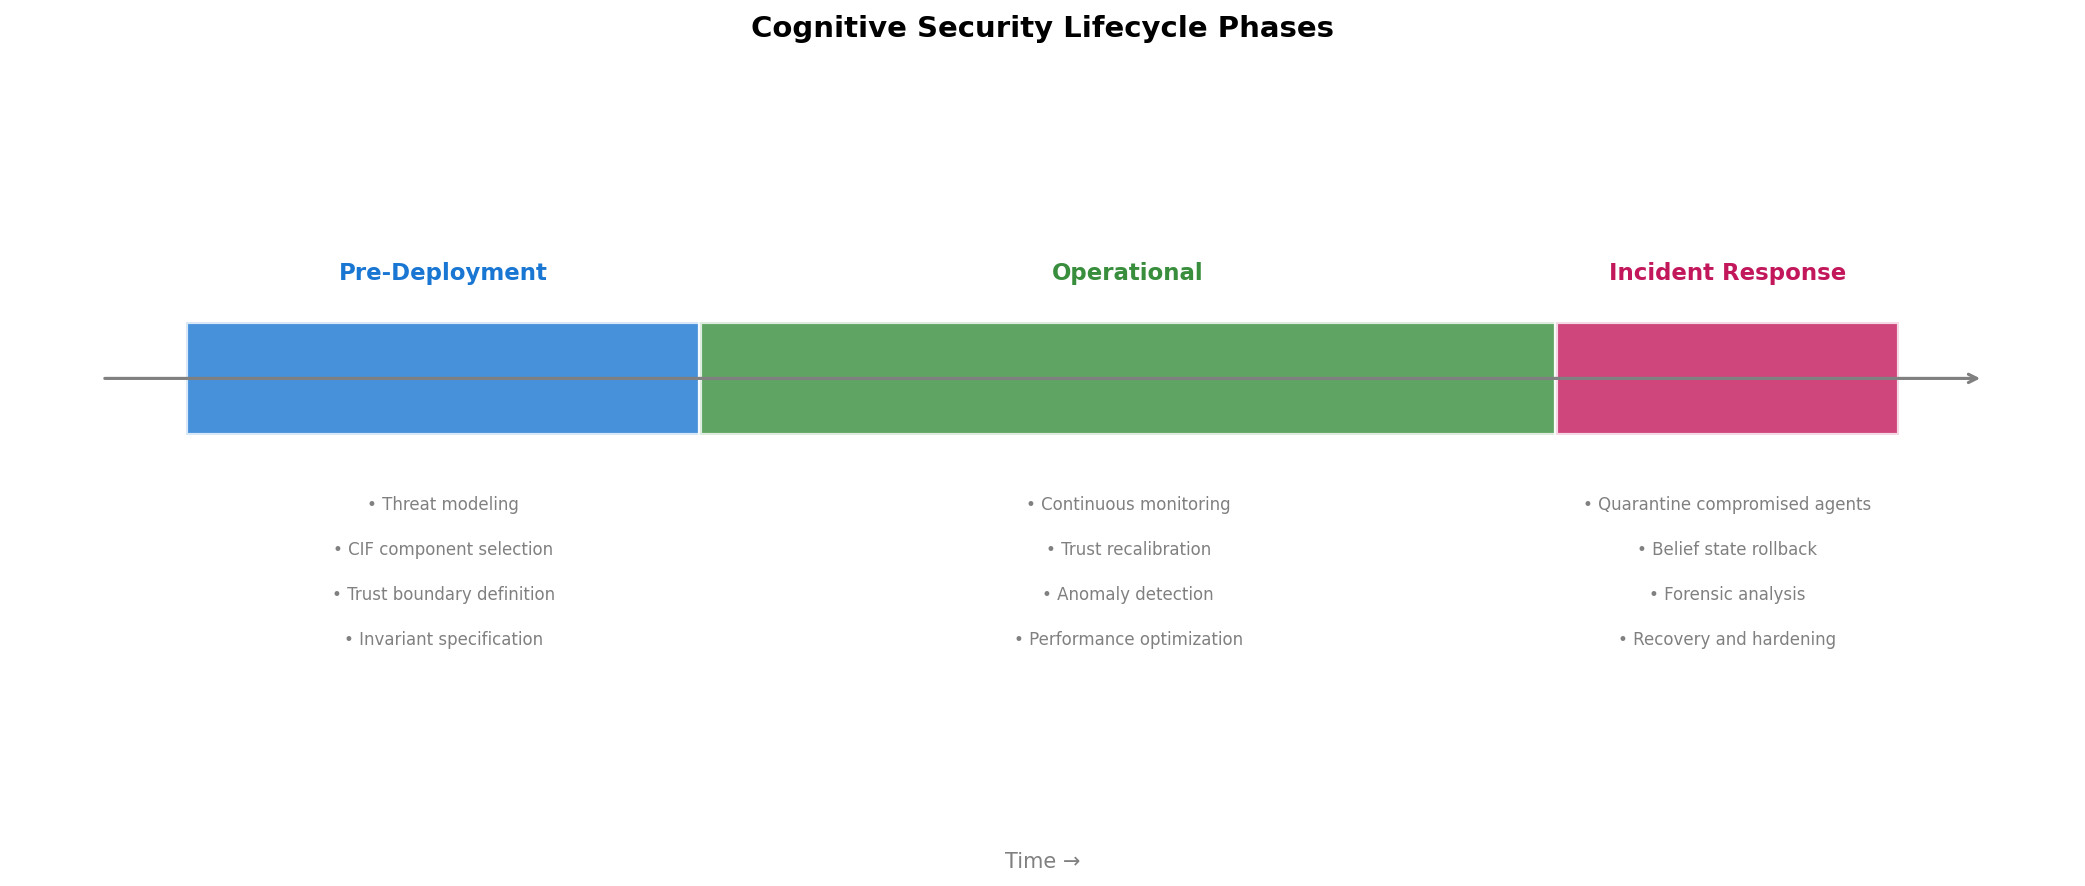
This unified paper (originally Parts 3 and 4 of the Cognitive Security for Multiagent Operators series) combines the practitioner deployment guide with a rigorous cross-domain application of the Cognitive Integrity Framework (CIF). **Practitioner Guidance (§1–§8).** Translates the formal results of Parts 1 and 2 into accessible engineering guidance: operator posture assessment, human oversight checklists, agent security invariants, deployment configuration, risk assessment, attack scenarios, subagent hardening, incident-response playbooks, monitoring strategies, cost–benefit analysis, common pitfalls, case studies, and operator risk frameworks. **Cross-Domain Applications (§9–§10).** The CIF-AD-OODA integration model is applied to analyze Goal Hijacking across ten critical domains. Cross-domain synthesis reveals three universal attack patterns and four novel defense extensions. This is Part 3+4 of a three-part series: - Part 1 (DOI: 10.5281/zenodo.18364119): Formal foundations and theoretical analysis - Part 2 (DOI: 10.5281/zenodo.18364128): Computational validation and implementation - Part 3+4 (this paper): Practitioner guidance and cross-domain CIF-AD-OODA applications
Overview source: Curated paper metadata.
Artifacts
Tracked documentation and PDFs served directly from this folder.
README AGENTS SKILL Metadata Extracted text Citation metadata
- cogsec_multiagent_3_practical_combined.pdf 1,389,206 bytes · extracted-text source
Extracted Images (9) — GitHub +3 more